The eight-day board
The plan was a target sequence for a showcase-ready MVP, one validated milestone per day. The diagram below is the target design — the shipped implementation kept the same engine/adapter ideas with a different substrate, and this page says so plainly.
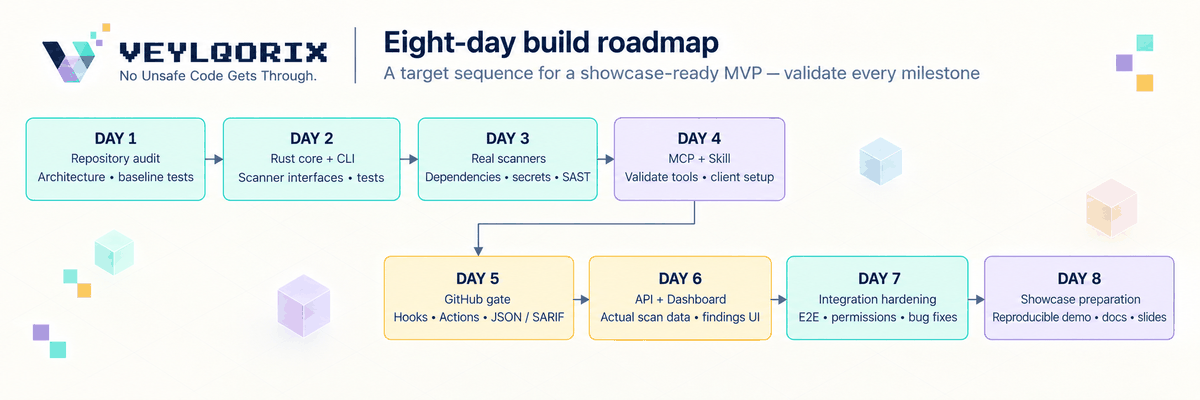
Eight-day build roadmap — target sequence, each milestone validated before the next.
Day 1
1 / 8
Repository audit
Architecture review and baseline tests — know what you are about to verify.
Day 2
2 / 8
Core + CLI
Scanner interfaces and a working command line, with tests.
Day 3
3 / 8
Real scanners
Dependencies, secrets, and static analysis — the evidence layer.
Day 4
4 / 8
MCP + Skill
Validate the agent tools and wire up client setup.
Day 5
5 / 8
GitHub gate
Hooks, Actions, and JSON / SARIF output for CI.
Day 6
6 / 8
API + Dashboard
Actual scan data and a findings UI on top of it.
Day 7
7 / 8
Integration hardening
End-to-end flow, least-privilege permissions, bug fixes.
Day 8
8 / 8
Showcase preparation
A reproducible demo, docs, and slides you can stand behind.
Shipped vs. the board
The board said “Rust core” on Day 2. What shipped first is a pnpm TypeScript monorepo — because a working, testable MVP beat a target-language stub. The gate logic, finding schema, and adapter architecture made it through intact — and the Rust core then landed on its own terms: a byte-compatible security engine with a TypeScript adapter, now on main.
Done
7 milestones landed
- Core engine with deterministic gate (0 PASS / 1 FAIL / 2 INCOMPLETE)
- Rust security engine crate + TypeScript adapter, byte-compatible, 60 cargo tests — on main
- CLI check is scanner-free (type, lint, tests): gate always INCOMPLETE (exit 2); secrets need scan
- CLI, MCP server, REST API, and web dashboard shipped and tested
- Reusable, SHA-pinned GitHub Actions gate with SARIF upload
- Portable agent skill for Claude Code, Codex, and Cursor
- Honest demo-mode dashboard that never fakes live data
Still open
4 items in flight
- Publish @veylqorix/cli to the npm registry — non-monorepo callers need it
- Publish @veylqorix/plugin (the scanner extension SDK) to the npm registry — same status as the CLI
- Owner setup for the release workflow: register the trusted publisher, push the first v* tag, and settle the engine-binary distribution story (the publish step fails closed until then)
- GitHub Actions branch-protection guide with screenshots
From advisory to enforced
Publish the CLI and plugin
Release @veylqorix/cli to the registry so repositories outside this monorepo can run the gate directly, and @veylqorix/plugin (the scanner extension SDK) so teams can extend the audit with their own scanners and checks. Both are consumed from source via workspace:* until publish.
Authoritative results
The engine crate and its TypeScript adapter are on main. Gitleaks delegation ( preferGitleaks) and cargo audit already live inside the engine, behind the byte-compatible protocol — the real binary now runs in CI so results stay authoritative.
Branch-protection guide
A screenshot-backed guide to requiring the gate status check, so the gate stops being advisory and starts blocking merges.