Verify the code your agents wrote. Before it ships.
Veylqorix independently verifies AI-generated and human-written code before it is committed, pushed, merged, or deployed. It orchestrates real scanners — dependency auditing, secret detection, license checks, static analysis, and test suites — normalizes their output into one finding schema, and turns it into a deterministic gate decision with auditable evidence.
$ veylqorix scan . --json
23 findings · 2 critical · 5 high · 8 medium · 8 low
CRIT secret: AWS access key in config.js:12 — AKIA…CDEF (20 chars, redacted)
HIGH vulnerable dependency: lodash@4.17.15
MED license risk: GPL dependency in an MIT project
Illustrative output. Exit 2 (INCOMPLETE) means degraded coverage — never a clean pass.
Four guarantees
AI coding agents now write a large share of production code — fast, plausible, and occasionally unsafe. Lint and CI pipelines were not designed to verify that volume. Veylqorix fills the gap:
Guarantee 01
Real evidence, no fabrication
Every finding, severity, and exit code comes from an actual scanner run. A check that cannot run is reported SKIPPED or ERROR with a reason — never a clean pass.
Guarantee 02
One engine, many surfaces
CLI, MCP, GitHub Actions, and the dashboard are thin adapters over a single core, so security logic exists in exactly one place and behaves identically everywhere.
Guarantee 03
Deterministic gate
Exit codes are stable — 0 PASS, 1 FAIL, 2 INCOMPLETE — so CI branching is predictable and auditable run to run.
Guarantee 04
Agent-safe policy
An AI agent cannot suppress findings or raise thresholds: exceptions must be documented, capped, expirable, and visible in the committed policy file and every gate report.
Where Veylqorix plugs in
Every surface is a thin adapter over the same core engine (packages/core), so there is exactly one place where security logic lives:
CLI
01Real scans, deterministic exit codes, safe dry-run hook installer. Not published to npm yet — run from dist/, with the Rust engine built from source.
MCP server
02Six validated tools, root-confinement + redaction. Requires pnpm build.
GitHub Actions gate
03Real scan + SARIF upload, all actions pinned to SHAs. Advisory until a branch-protection rule requires the check.
Agent skills
04Portable SKILL.md plus MCP configs for Claude Code, Codex, and Cursor.
Dashboard
05Live scan data from the API; clearly-labeled DEMO MODE when the API is down.
Plugin SDK
06Scanner extension SDK: add your own scanners and quality checks; their findings flow into runAudit and the same gate. Not published to npm yet.
Honest note
The gate and the CLI hooks are advisory until enforcement is in place — a branch-protection rule that requires the check, or a published CLI. Findings are produced and the check fails; a merge can still be forced. That is stated everywhere, never hidden.
Release posture
Release-readiness hardening, validated against the engineering docs: GitHub Actions pinned to commit SHAs, the transitive postcss and sharp vulnerabilities patched in place via pnpm overrides, and the Rust engine clean under cargo-audit (37 crates, 0 findings). Publishing is gated on npm provenance attestation; nothing is on the registry yet — run from source.
Scanner adapters reuse real tools
| Scanner | Backed by | Offline? |
|---|---|---|
| Dependencies | npm audit (Node) / pip-audit (Python) | optional |
| Secrets | Rust engine secret scanner (offline, 9 families) — TypeScript fallback, redacted values | yes |
| Licenses | manifest-level license checks, copyleft risk | yes |
| Quality | tsc, eslint, ruff, project test scripts | no |
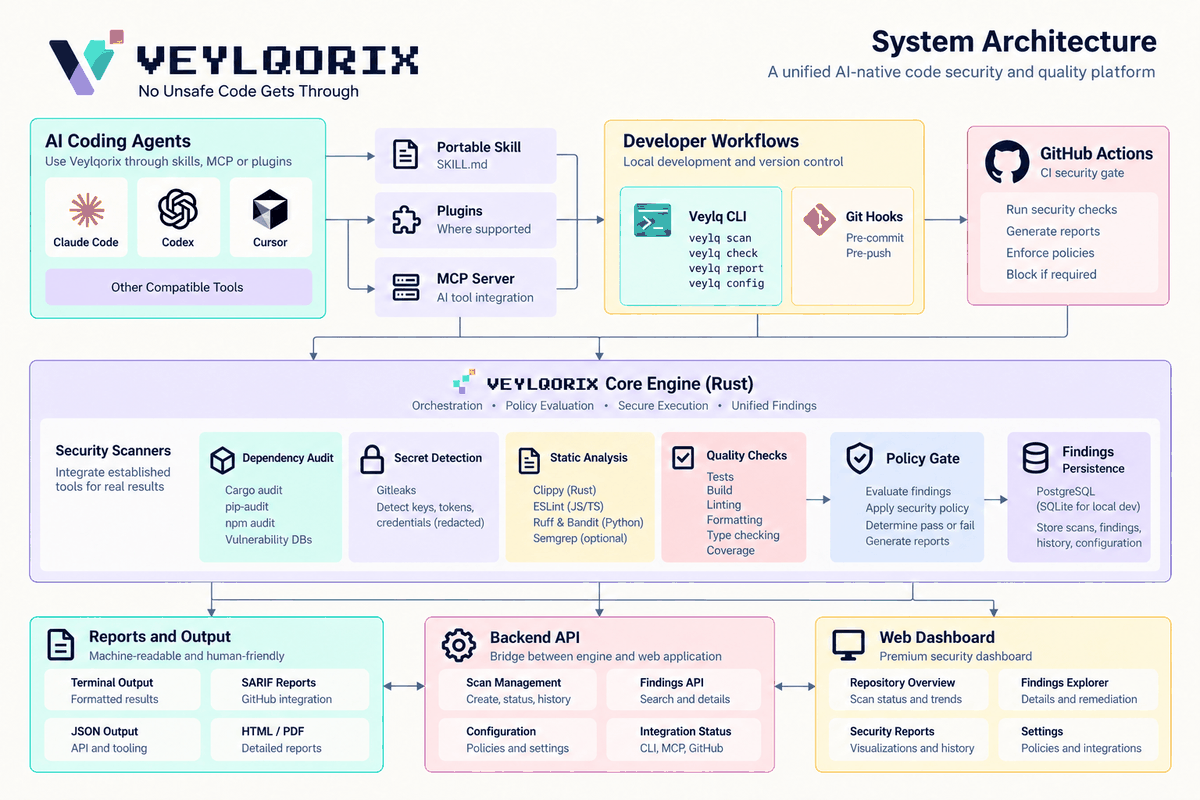
System architecture — entry points reach one core engine; results fan out to CLI, API, and CI surfaces.
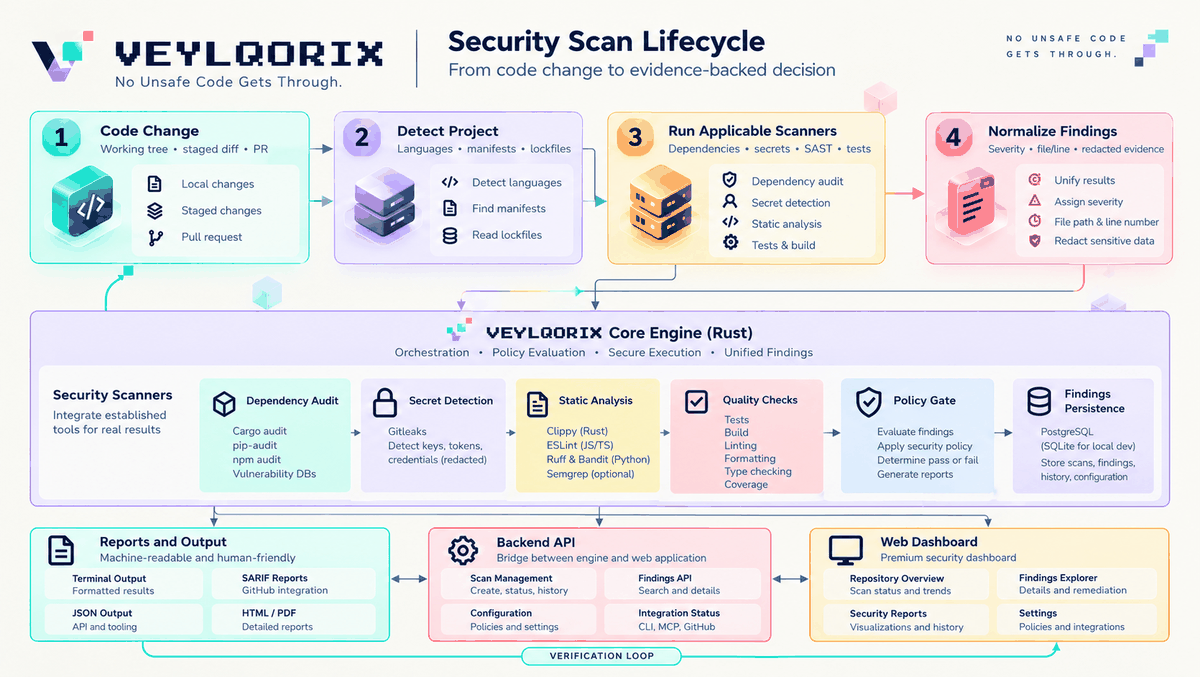
Scan lifecycle — normalize before judging, gate failures are first-class, verify don't trust.
What Veylqorix is not
Read this first
- Veylqorix reports what its scanners found. It does not certify the absence of vulnerabilities or secrets.
- A scanner that cannot run makes the gate INCOMPLETE (exit 2) — degraded coverage is surfaced, never green-washed.
- Regex secret detection has false positives and negatives; it complements tools like Gitleaks, it does not replace them.
- License scanning is manifest-level, not a transitive license audit. A clean quality check is not a security certification.
A check that cannot run is reported SKIPPED or ERROR with a reason. Veylqorix surfaces incomplete audits instead of green-washing them.
The full story, in three places
Story
How it was built
Five diary-style posts: the gap, the eight-day board, INCOMPLETE, one engine, and the sync loop.
Changelog
0.1.0 → 0.1.1, then Rust
Every release, every group of changes — now including the Rust security engine wired in through a TypeScript adapter.
Tour
Inside the platform
CLI, MCP, API, dashboard, GitHub gate, security model, and community ground rules.